Can You Run WP Remote’s Firewall and Wordfence at the Same Time?

WP Remote and Wordfence running on the same WordPress site, showing the recommended setup of one primary firewall with complementary malware scanning and login security instead of two overlapping WAFs.

WP Remote and Wordfence can be installed on the same WordPress website, but there is an important distinction between: and: Those are not the same decision. WP Remote currently includes: Its current API documentation also shows that the firewall can be enabled per site and that bot protection can be switched on or off independently. … Read more
Wordfence High Sensitivity Scan Runs for Hours and Then Fails

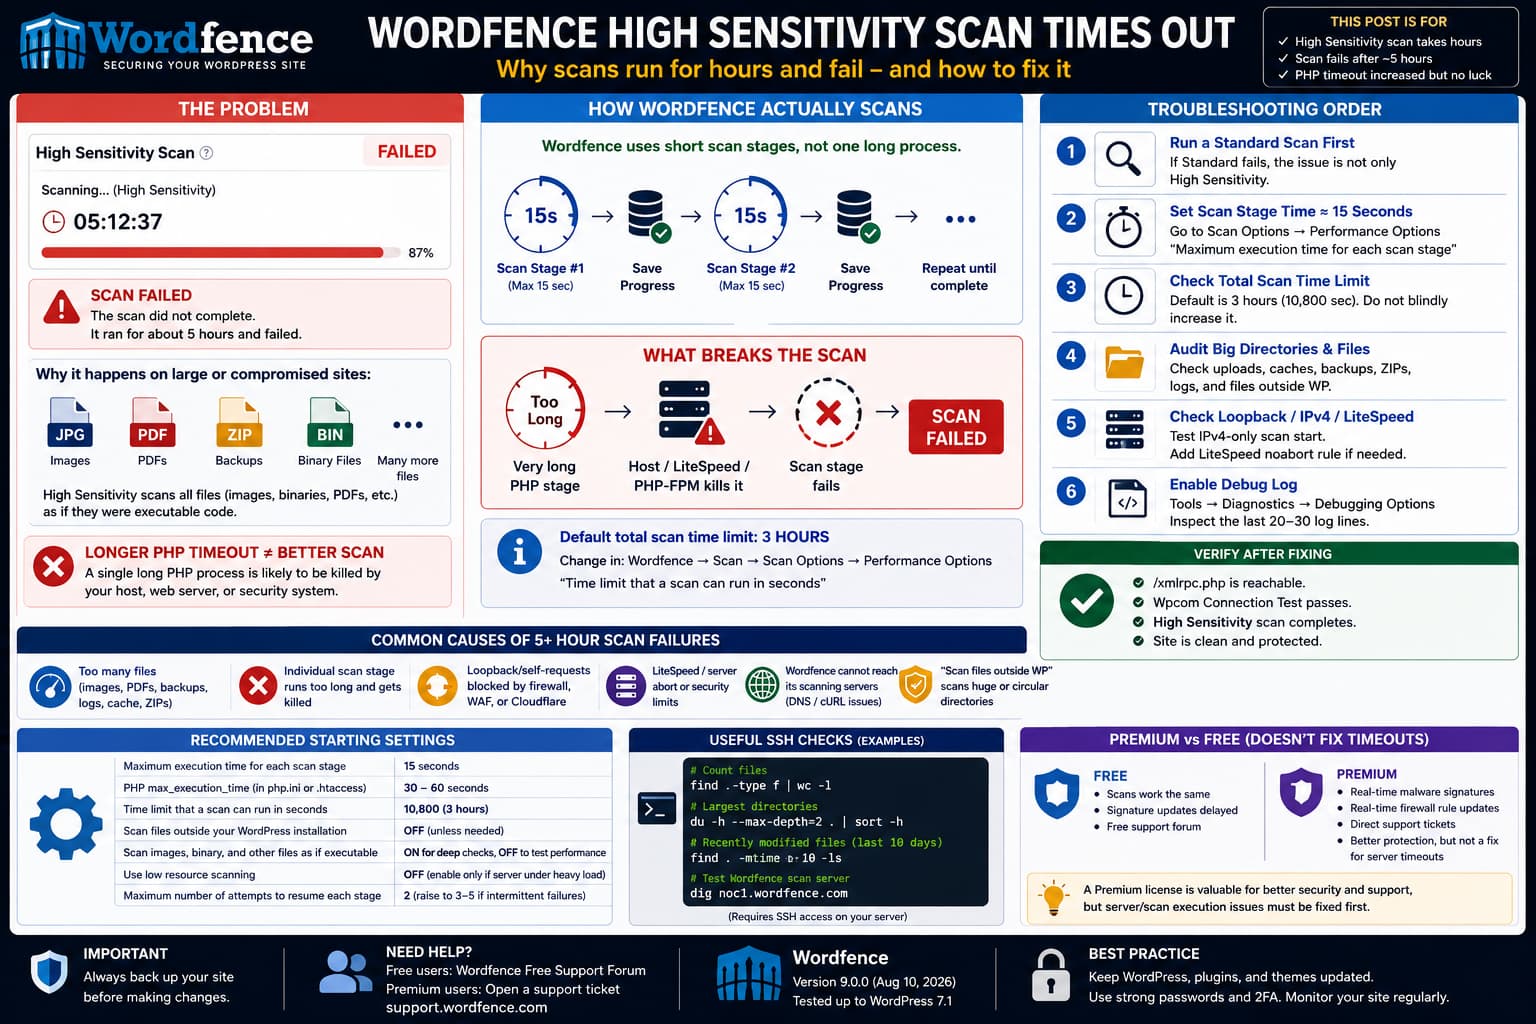
Wordfence High Sensitivity scan running for hours and timing out, with short scan stages, large image and backup directories, and server timeout troubleshooting shown as the solution.

When a Wordfence High Sensitivity scan runs for several hours and eventually fails, increasing PHP’s execution time is not necessarily the correct fix. Wordfence does not expect one PHP process to remain alive for the duration of an entire scan. Its scanner works as a sequence of shorter requests. Each scan stage performs some work, … Read more

Wordfence Plugin Keeps Disappearing After a WordPress Hack

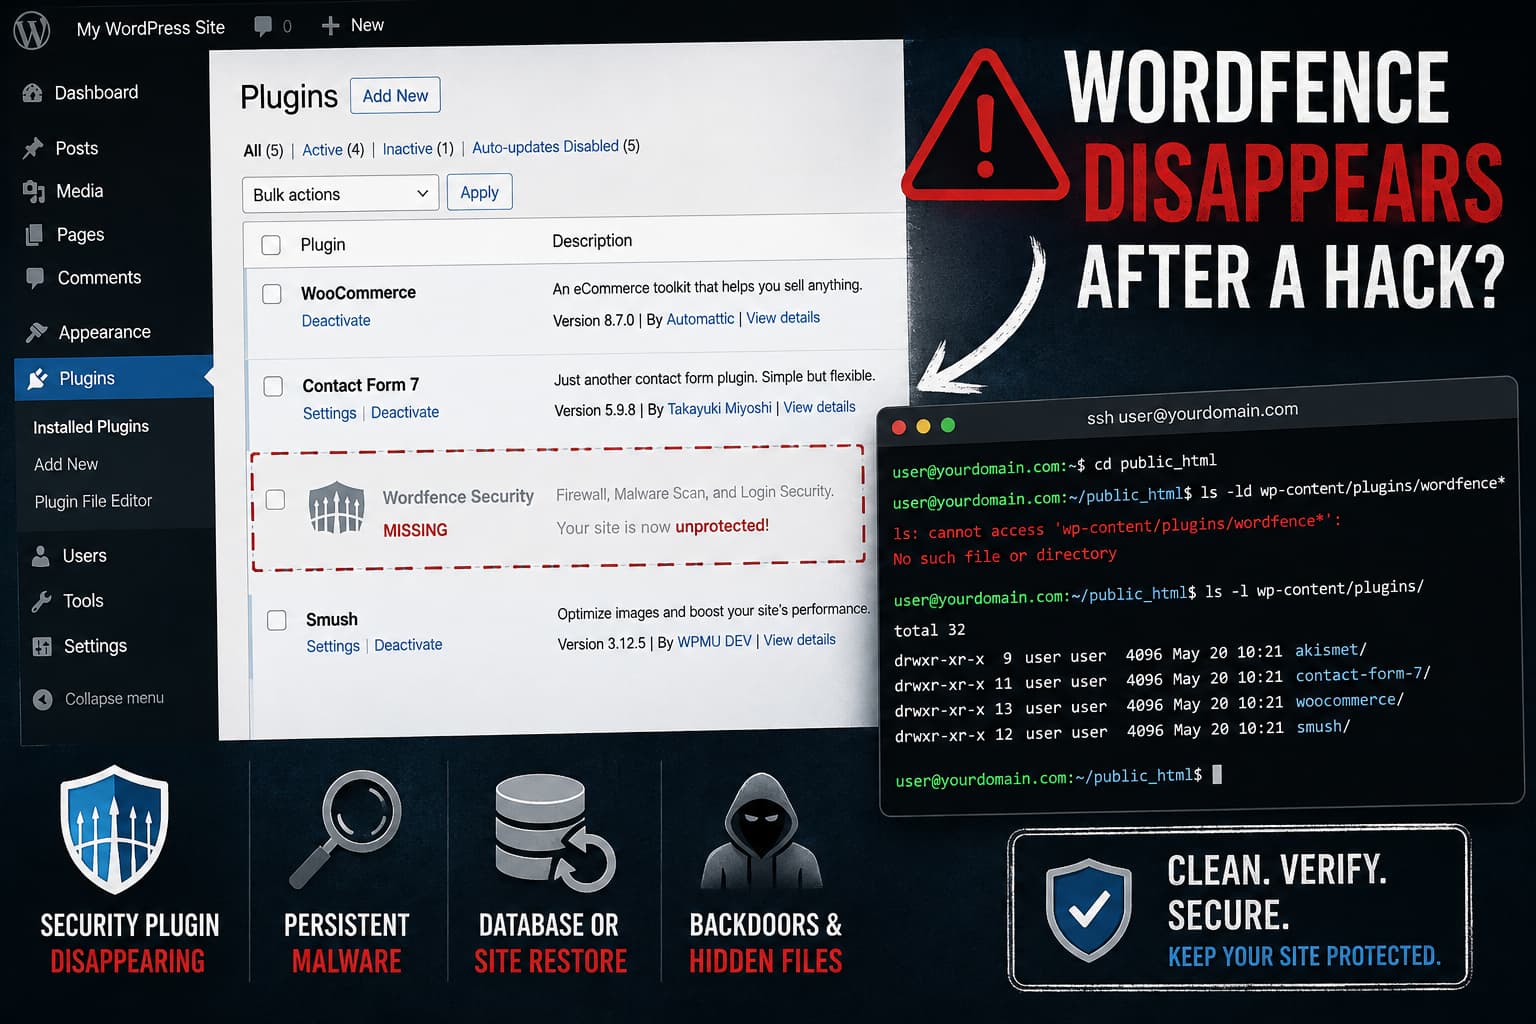
WordPress plugins screen showing the Wordfence plugin disappearing while a terminal checks the Wordfence plugin directory.

If Wordfence is installed after cleaning a hacked WordPress site and then disappears again hours later, treat the site as still compromised until you can prove otherwise. A normal plugin or theme conflict might deactivate a plugin, but it should not normally delete or rename the entire wp-content/plugins/wordfence/ directory. Malware can do exactly that. Wordfence … Read more

Product Feed PRO: “Skipping Scheduled Feed Generation: Previous Run Is Still Processing”

Product Feed PRO warning that scheduled feed generation was skipped because a previous run is still processing, showing how to identify a stale WooCommerce Action Scheduler batch and safely reset the feed.

After updating Product Feed PRO for WooCommerce by AdTribes, you may start seeing this warning every day: The wording sounds alarming, but the message itself is actually a safety check. Product Feed PRO uses WooCommerce’s Action Scheduler to refresh feeds in batches. If a new scheduled refresh begins while the plugin believes the previous refresh … Read more

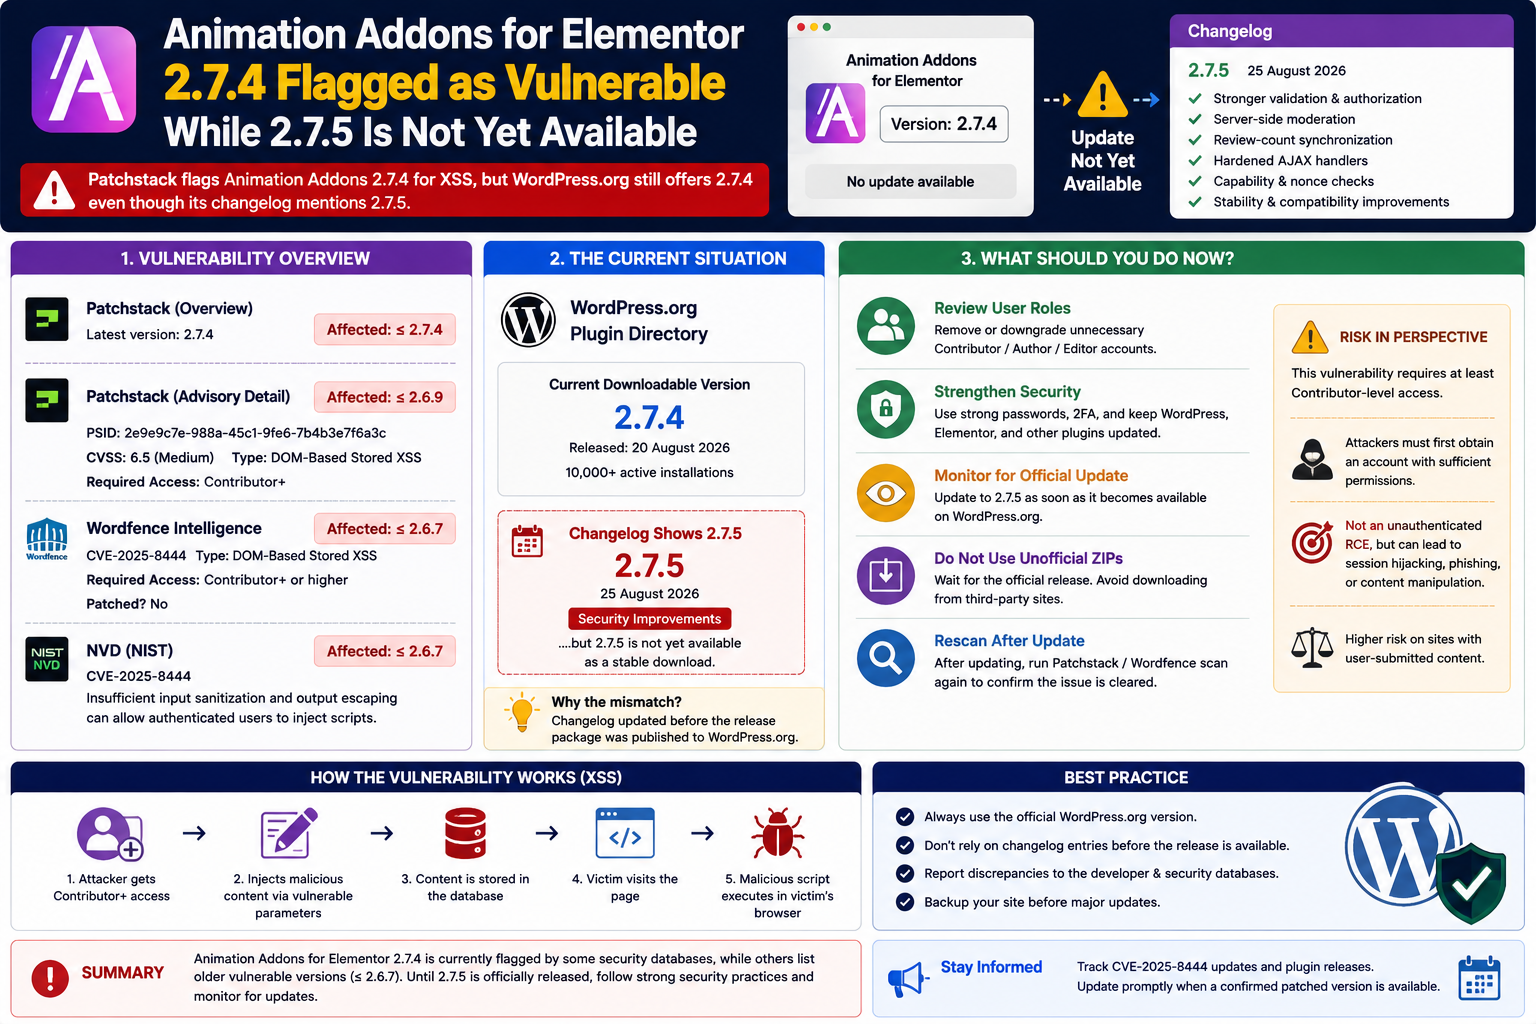
Animation Addons 2.7.4 Is Flagged as Vulnerable, but WordPress.org Still Doesn’t Offer 2.7.5

Animation Addons for Elementor 2.7.4 security warning showing conflicting Patchstack, Wordfence, and NVD affected-version ranges while WordPress.org lists a 2.7.5 security changelog but still only offers version 2.7.4.

There is currently a confusing security situation around Animation Addons for Elementor. A site owner running: may receive a Patchstack warning stating that the plugin is affected by a Cross-Site Scripting vulnerability. At the same time: while the plugin’s own WordPress.org changelog already contains: with several security-related changes. That raises an obvious question: If 2.7.4 … Read more

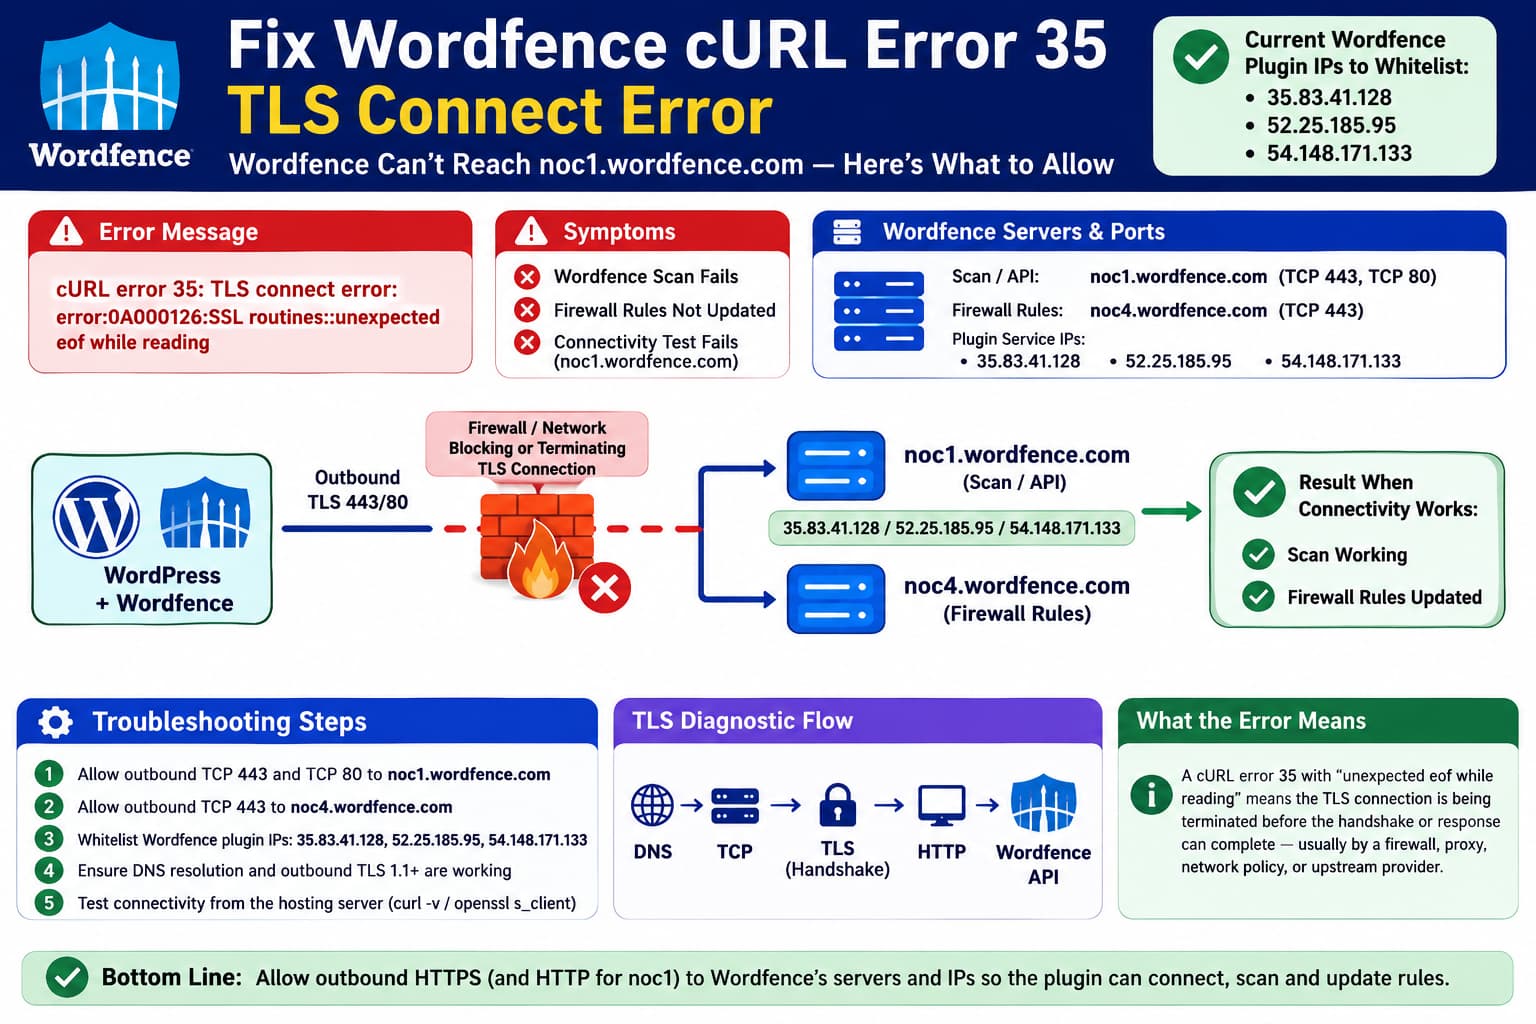
Wordfence Scan Fails With cURL Error 35 and “Unexpected EOF While Reading

Wordfence cURL error 35 caused by a failed TLS connection from a WordPress hosting server to noc1 and noc4 Wordfence services, with current IP addresses and firewall troubleshooting steps.

A Wordfence scan may fail with: and the same error can appear under: when WordPress tries to connect to: If firewall rules also stop updating, this becomes more than a scanner issue. The combination: strongly points to an outbound network/TLS problem between the web server and Wordfence’s infrastructure. Wordfence’s documentation confirms that scans require the … Read more

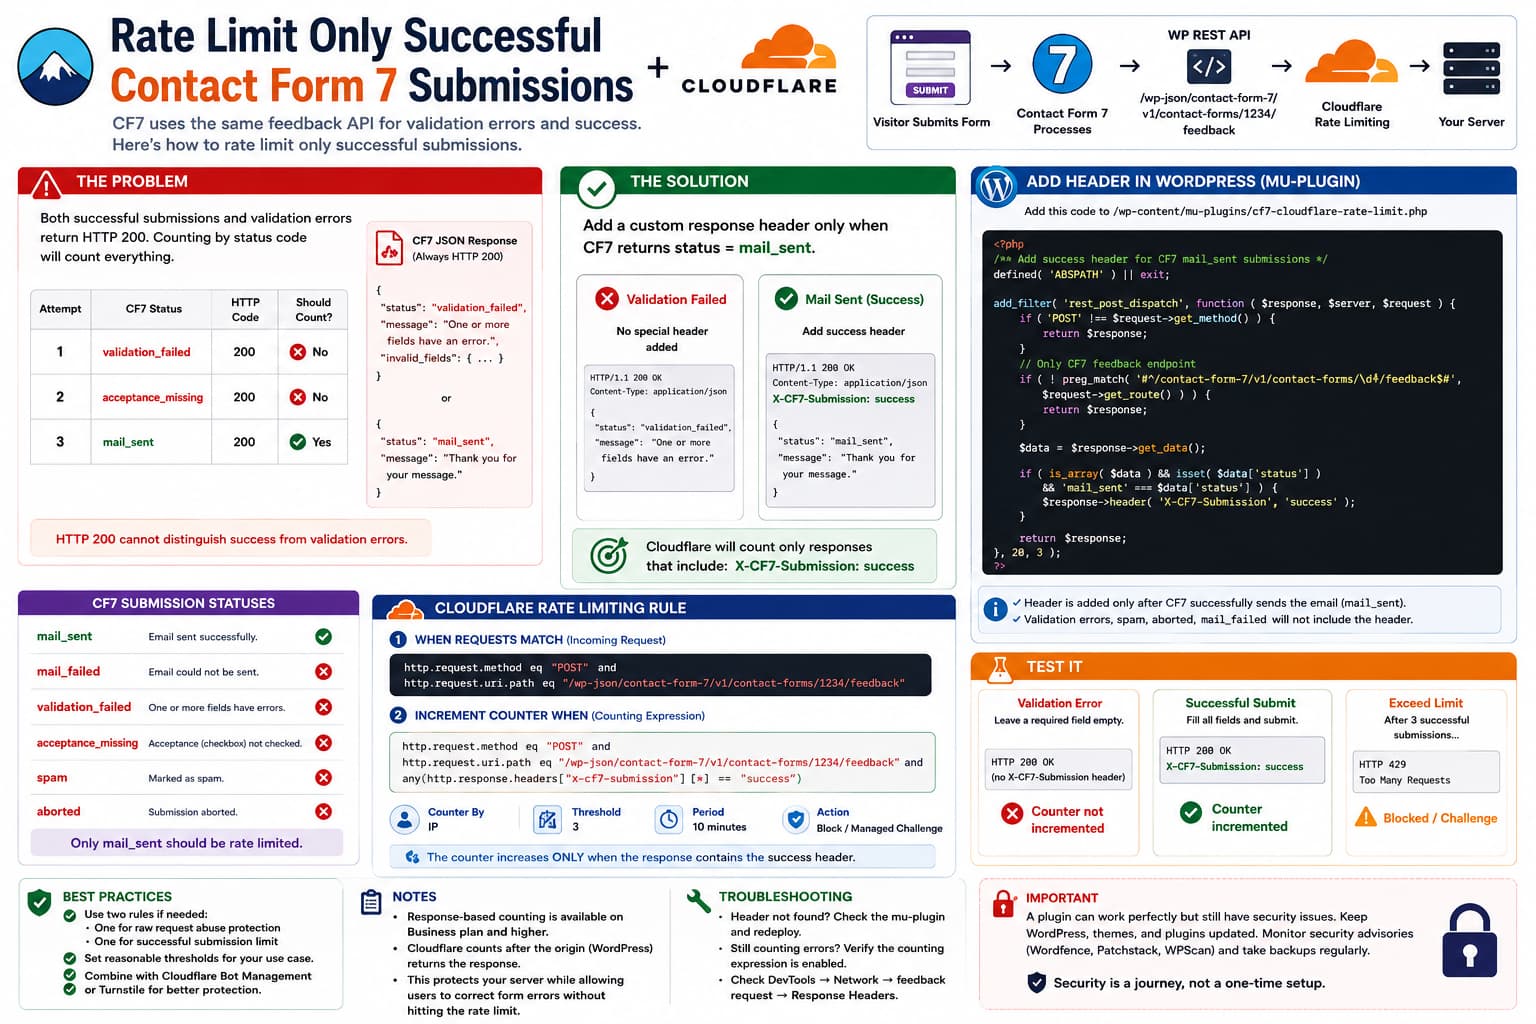
Rate Limit Only Successful Contact Form 7 Submissions With Cloudflare

Contact Form 7 and Cloudflare rate limiting setup where validation failures return HTTP 200 but only successful mail_sent responses receive a custom header and increment the rate-limit counter.

If Contact Form 7 submits through: /wp-json/contact-form-7/v1/contact-forms/1234/feedback it is tempting to create a Cloudflare rate-limiting rule such as: POST requests to /feedback→ maximum 3 requests per 10 minutes There is a problem. Contact Form 7 uses the same REST endpoint for both: Valid submission and: Validation failure So a visitor who accidentally misses three required … Read more